Results (1375 found)
Page
Cyber Security | Secure Intercom Solutions
Cyber Security A Question of Trust Protecting and securing customer data is essential to earning the trust of our users, as the growing multitude of new digital processes offers a growing attack surface to cyber criminals. Malicious software, data fraud and phishing for passwords or access credentials are only a few of the threats that users have to be protected against. Today’s Commend system security is firmly rooted in 50 years of experience in designing and perfecting Intercom security and communication technology. To fend off possible attacks, Commend has made IT security in general and cyber security in particular a top priority. We are fully aware of our crucial responsibility where the safety and trustworthiness of our security and professional communication solutions are concerned. As a result, we always endeavour to communicate and demonstrate our commitment as a trustworthy market leader to promote our collective knowledge and shared experience. For this reason we develop our solutions with security and data protection in mind, so as to ensure the best possible protection of our customers’ data and infrastructures. From the initial product design to its implementation and after-sales service, ‘ Privacy and Security by Design ’ is the guiding principle and solid promise to our customers that every product feature and function is tested against. NDAA/TAA Compliance Vulnerability Disclosure Policy Cyber Security Space - cLibrary Certified to IEC 62443 ISO 27001 All-around Cyber Defense Privacy and Security by Design Active Device Management Upgrade Subscriptions Always Stay Well Protected How Commend Handles Cyber Security & Vulnerabilities Discover how Commend prioritizes cyber security and keeps your systems protected. In this video, our Lead Security Architect explains: How to report vulnerabilities The process of vulnerability management and security notifications Our IEC 62443-certified secure development practices Internal and external security testing procedures How to stay updated NDAA/TAA Compliance Commend USA is pleased to confirm that its entire product portfolio is in full compliance with the National Defense Authorization Act (NDAA) and the Trade Agreements Act (TAA). Learn more Vulnerability Disclosure Policy The Commend Security Advisory Program Commend International is very serious about the security of its products and services, and we greatly value the contribution of the security community. We have therefore implemented a coordinated process for disclosing security vulnerabilities. All customers and security professionals are invited to participate and register for the Commend Security Advisory Program. Learn more World's first Intercom Company IEC 62443 certified Certified to IEC 62443 Secure Product Development Lifecycle assessed and monitored according to IEC 62443-4-1. Learn more Cyber Security begins at home ISO 27001 Information Security Management At Commend, we put all our efforts to provide customers with the best cyber security possible. Learn more Security for Products and Applications All-around Cyber Defense The global security-specific hardening of local and cloud-based Commend systems spans several basic levels. Learn more How does it Work? Privacy and Security by Design The basic principle is easy: providing the best possible protection of both transferred data and ‘stationary’ data against unauthorised access in order to ensure the availability of products and services. Commend products are always designed, developed and incorporated in customer solutions in accordance with these security criteria. Learn more Add-on service Active Device Management A new set of services offered by Symphony Cloud , designed to provide advanced device management capabilities, including automatic firmware updates, active monitoring and much more. Learn more Keep your system up-to-date and secure Upgrade Subscriptions Ensure that you always use the latest software, which reduces maintenance and support costs for both the customer and the service provider. Learn more 10 Recommendations for Risk Assessment We recommend carrying out a risk assessment before planning and installation. 10 Recommendations Contact us Want to learn more about Cyber Security and system hardening at Commend? Simply get in touch with us. Download Documents, Guidelines, Certifications,... on the topic of Cyber Security Cyber Security and Cyber Defense Get Expert Cyber Security Insights Discover how collaboration across the product supply chain enhances cybersecurity for your Commend system. Learn about potential risks, effective measures, and best practices to safeguard your devices, services, and network infrastructure. Download this essential cybers ecurity whitepaper for expert advice and guidelines.
News
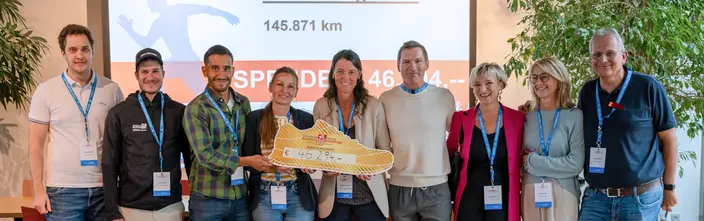
Salzburg Business Run Charity Challenge 2025
This year’s Salzburg Business Run Charity Challenge , launched in 2018 in Salzburg by Commend together with SKIDATA , achieved another record in its eighth year. The initiative transforms employees’ running kilometers into donations for charitable causes. With remarkable dedication, 647 participants from 30 teams covered an incredible distance of 152,819 kilometers over three months. Their athletic effort translated into a new record donation of €46,294 for Verein JoJo , supporting children from families affected by mental health issues in Salzburg. Nearly 70 colleagues from Commend formed our team and contributed to this success with athletic determination and strong teamwork. Congratulations to this year’s winning teams, recognized for achieving the highest average distance per participant: Bio-Nahrungsmittel Produktions- und Handels GmbH – 1st place ( 553.42 km per participant ) Industriellenvereinigung Salzburg – 2nd place ( 462.91 km per participant ) STEPA Farmkran Gesellschaft m.b.H. – 3rd place ( 356.78 km per participant ) The award ceremony and donation handover to Verein JoJo recently took place, as tradition, at Commend International , bringing together representatives from all participating teams.
News
Technology that never stops growing
Technology often becomes outdated within years, but Commend has taken a different approach. With our Evergreen Technology philosophy, we ensure that intercom and communication systems remain reliable, secure, and continuously up to date for years or even decades. At the core of this concept are three principles: Regular software updates extend the life of installed systems by introducing advanced innovations. AI Cleans Voice from Noise , which filters background sounds to deliver crystal-clear conversations even in loud industrial environments, is available for all Symphony MX devices with the latest update. Exceptional backward compatibility . Our new adapters allow new modules to replace those in long-serving installations – from emergency call points to ticketing machines – without reconstruction. This enables our customers to benefit from features like AI and cloud connectivity without replacing their entire system. Sustainable product design ensures that every solution follows a “ Privacy and Security by Design ” approach, complying with international standards such as ISO/IEC 27001 and EN/IEC 62443-4-1 . This combination of technical continuity and cybersecurity resilience offers lasting investment protection and reduced environmental impact. By extending lifecycles instead of replacing systems, Commend’s Evergreen Technology embodies long-term sustainability in secure communication.
Page
Project Consulting Commend Türkiye
Project Consulting How can we help you? Your ideas. Your requirements. An overall solution. Are you looking for assistance with a new project? Do you have a technical question or need help in deciding how to expands your existing system? Contact us to take advantage of our comprehensive range of services. If you are on the lookout for an individual security/communication solution We provide individual advice on finding the best security and communication solution to suit your requirements. We will work with you to develop a plan for your individual system solution. You can take full advantage of our long-standing experience resulting from more than 150,000 installations worldwide. We will support you all the way in implementing your solution, taking care of the individual steps. Users will receive full training from our experts to ensure your system will run smoothly and is used to its full potential. Of course, we also provide a wide range of system maintenance and servicing options, as well as technical support whenever you need it. If you intend to extend your existing system Uncompromising backward compatibility is a hallmark of our systems. It allows for extending existing legacy systems with latest technology, even enabling full networking of sites running different systems. We provide assistance in planning and installing extensions and take great care to ensure long-term economical efficiency. If you need a custom station or software We design and manufacture intercom stations and emergency call points according to your requirements – whatever these are (Features, Material, special Size e.g. for existing back boxes). We write special software for ComWIN and the Intercom Client, browser interfaces, ... We programme interfaces to other systems. Learn more about our Customized Solutions Support Constant availability is essential in security and communication systems. You can rely on us being there whenever you need assistance. Our worldwide technical teams are standing by to provide telephonic or on-site support at any time, quickly and reliably. Contact us Training Sign up for our expert training course and become a Commend System Professional. Your local Commend Partner will be glad to provide further details on our course schedule. Training area Software & Documentation Leverage our on-line knowledge base as an extensive reference to find answers to your questions. Here you have access to important information about our systems, from installation instructions to hints on how to optimise your configuration and download links to current software versions. cLibrary 23 Sales Organisations worldwide Always there, wherever you are America – Europe – Africa – Middle-East – Asia/Pacific
Page
10 рекомендаций | Руководство по оценке рисков
Мы рекомендуем учитывать следующие моменты при проведении оценки рисков Оценка рисков Кибербезопасность Требования и цели безопасности , например, функциональные и нефункциональные системные требования Системная или сетевая архитектура и инфраструктуры , например, с использованием сетевой карты и плана компонентов, которые показывают, как настроены и взаимосвязаны активы Сервисы и приложения , включая данные и протоколы, например, приложения с особо конфиденциальными данными Процессы обработки данных , включая параметры ввода и вывода, такие как бизнес-процессы, рабочие процессы компьютера и рабочие процессы приложений Зависимости между приложениями и процессами , например, обработка особо конфиденциальных данных Оценка воздействия , например, определение последствий в случае потери конфиденциальных данных, анализ угроз с помощью модели и т.д. Технические меры , например, выбор подходящих компонентов безопасности, таких как межсетевые экраны, системы обнаружения вторжений или системы контроля физического и логического доступа Организационные меры , например, управление непрерывностью бизнеса и управление аварийным восстановлением Государственные законы и постановления , касающиеся минимальных требований контроля безопасности Документированная или неофициальная политика, процедуры и руководящие принципы Для получения дополнительной информации, пожалуйста, обратитесь в Ассоциацию аудита и контроля информационных систем, ISACA ( www.isaca.org ) или соответствующий стандарт ISO для управления рисками в ИТ-системах ISO 27005. Кибербезопасность
Page
All-around Cyber Defense | Secure Communication Systems
All-around Cyber Defense for Products and Applications Commend Defense In-Depth-Strategy Cyber Security Commend Defense In-Depth-Strategy is based on the principle of ensuring IT security in all areas (environments, design, implementation and integration) to eliminate vulnerabilities and attack vectors. In practice, this means: IEC ISO 27001:2022 certified , company-wide information management system ( Learn more ) World’s first Intercom company certified to IEC 62443: Tested and certified by globally recognized cyber security certification service provider TÜV SÜD Commend development teams develop and implement secure communication and automation solutions in accordance with the IEC 62443 Part 4-1 ( Learn more ) Use of secure standard Internet protocols: TLS and SSH data transfer security for HTTP and MQTT Secured SIP network access via 802.1x auth and 802.1q VLAN connections Use of secure cryptography by default: Encrypted, login-protected communication via Commend signed device certificates Commend Public Key Infrastructure (PKI) as a basic ‘Root of Trust’ (for generating and signing of device and application certificates) to ensure mutually login-protected, encrypted communication Security-focussed development processes: Multi-level monitoring and testing Regular test cycles before product releases and after updates Vulnerability monitoring and disclosure policy: Pen tests by external security testing bodies or ethical hackers Coordinated processes for reporting and disclosing vulnerabilities Commend Security Advisory Program: summaries of notifications, affected products, software updates, workarounds or mitigation, change log, etc. The global security-specific hardening of local and cloud-based Commend systems spans several basic levels: Devices Data Applications Platform Device Security Physical access protection Vandal-resistant Video Intercom stations (with camera) Tamper detection via electromechanical contact USB and port debugging protection Access Control Systems Secured network access 802.1q VLAN standard (network segmentation) 802.1x secured login Commend IP Secure Connector (automatic network cut-off in case of manipulation) Terminal device security Offline capability, includes SIP call and door call functions Unique system login credentials for each individual device SSH remote maintenance functions disabled by default SHA and BCRYPT salted passphrase, encrypted access credentials Back to overview Data Security Data transfer protection Encrypted, login-protected communication settings TLS v1.2+ used exclusively with Secure Cipher Suites (> 128-bit) X.509 ECC NIST P-384 Commend device certificates Protection of stored data Use of MS Azure for database and data storage via PaaS Secured access to Azure data storage via device-specific SAS tokens Powerful 256-bit latest-generation AES data encryption SHA and BCRYPT salted password hashes (> 256-bit) Back to overview Application Security VirtuoSIS application security Offline capability, includes SIP call and door call functions Support of multiple instances: enables service redundancies as an emergency fallback solution Application security for devices Offline capability, includes SIP call and door call functions Enforced change of default login credentials upon first login Password minimum requirements: 12 characters Detection of brute-force login attacks Secured network ports Back to overview Platform Security Cloud platform-security OAuth Identity and Access Management (IAM) Azure Security Center Monitoring Azure KeyVault Secrets Management Azure Storage Service Encryption (SSE) Database Transparent Data Encryption (TDE) Open source and vulnerability management Use of proven de-facto standard libraries for logins and encryption Contribution to open source applications (e.g., Asterisk, BareSip, Mosquito, Wireshark) Continuous vulnerability scanning and monitoring Commend Security Advisories Secure default Internet protocols with focus on compatibility and security Back to overview
Page
Infrastructure Options – From On-Premise to Cloud
Infrastructure Options On-Prem? Cloud? Combination? No Server? The Choice is Yours Symphony Platform You can choose between a purely cloud-based infrastructure, servers that are hosted on site or in the data centre, or you can combine and use both. Depending on size and requirements, a solution with Symphony Mesh and without servers is an additional option. The choice is also available for existing systems. Our customers know and appreciate the Commend Evergreen technology, which enables them to connect their systems to the latest technology and operate them on the latest infrastructure. Symphony Cloud On-Prem Mesh Bridge Overview in 60 seconds The Future of Intercom Symphony Cloud Our cloud-based solution platform is built on highly scalable cloud infrastructure, powerful software and extensive features, with the clear aim of harnessing the power of current and future cloud services incl. AI. Symphony Cloud offers the right service for every size and requirement. Solutions can be purely cloud-based or combined with on-prem servers. Current Cloud Services Device and System Management Mobile Client with Apps for iOS and Android Web Client for Browsers incl. Control Desk Features Ivy – Virtual Intercom Voice Assistant Learn more Reliability in-house Symphony On-Prem With Commend VirtuoSIS, the world’s first completely software-based Intercom server, our solutions integrate seamlessly into the flexible, dynamic world of virtual IT environments (VMware vSphere, Microsoft Hyper-V and Nutanix Acropolis) and is at the core of our hardware servers S3/S6 , where they bring all their benefits and technical talents to bear: ultimate functionality and business-critical high availability, the central hallmarks of Commend solutions. On-Prem Features Extensive options and functions for control desk management (hardware and software solutions) The whole world of interfaces, integration possibilities, controlling and automatisation – Integration Zone All data is kept on the customer’s premises (or in their data centre) Cloud services can be used with Symphony Bridge Comes with the feature set of more than 50 years of development and experience About VirtuoSIS Autonomous and intelligent Symphony Mesh Commend devices of the latest “Symphony MX” and “Symphony BF” generation come with enough built-in intelligence to make a server unnecessary. Networked in free direct interplay, they form an intelligent autonomous communication network (registrarless) that is cost-efficient and ideal for smaller-sized applications. Extensive Commend Intercom functionality provides features from call answering and forwarding to video, remote control, Unified PA, redundancy and others. These make it easy to custom build solutions to support operational and security-critical applications and processes. Especially the unique so-called “action sequences” allow Commend IP devices to be programmed for functions and controls that would normally require a fair amount of server intelligence. Symphony Mesh Details A powerful connection Symphony Bridge The Bridge opens the world of on-premise solutions to Symphony Cloud services such as mobile iOS and Android clients or the Web Client that provides convenient call management in a browser window. Combining both architectures enables all-new solutions that bring together the best of both worlds. Nowhere does innovation progress at a faster pace than in the Cloud. We have some great things planned, with our next Symphony services already in the works or being evaluated in selected pilot studies. With Symphony On-Prem and Symphony Bridge access to this world of new possibilities is just a click away. Learn more
Page
NDAA and TAA compliant Intercom Systems
Trusted. Communication. Always. For Better Serving the US Public. Commend Intercom Systems Fully NDAA/TAA-Compliant Cyber Security In line with its strong corporate commitment to providing “Trusted. Communication. Always.”, Commend invests a lot of care and attention in ensuring product security both on the hardware and software level. Commend components, products and solutions are developed and manufactured from the ground up on the principle of “Privacy and Security by Design”. This is evidenced by a series of relevant audit-based certifications. They range from full ISO 27001 certification of the entire R&D and production environment to IEC 62443-4-1 for specific development processes. Existing or potential customers of Commend Americas that rely on this high level of product security include governmental agencies such as the U. S. Department of Defense or its affiliates. To them Commend USA is pleased to confirm that its entire product portfolio is in full compliance with the National Defense Authorization Act (NDAA) and the Trade Agreements Act (TAA). Full NDAA/TAA compliance is ensured on several levels: All products are produced exclusively at the Commend facilities in Salzburg, Austria, which eliminates the need for OEM sourcing. Commend has extensive product development policies and guidelines in place, which explicitly cover the NDAA requirements (among many others). All software used for and in Commend products is developed and implemented in-house in accordance with stringent and regularly audited cyber-security standards. Commend USA, through its related company, Commend International GmbH in Salzburg, Austria, certifies compliance of its product portfolio with all applicable requirements under NDAA/TAA . Certificates & Declarations What is NDAA? The National Defense Authorization Act (NDAA), specifically under Sections 889(a)(1)(A) and 889(a)(1)(B), imposes a prohibition on federal agencies, their contractors and grant or loan recipients to procure or use certain “telecommunication and video surveillance equipment or services” from specific Chinese companies. The banned items must not be used in “a substantial or essential component of any system, or as critical technology as part of any system.” This ban covers telecom products produced by (among others) Huawei Technologies Company and ZTE Corporation, and video surveillance and telecom equipment produced by Hytera Communications Corporation, Hangzhou Hikvision Digital Technology Company, or Dahua Technology Company. What is TAA? The Trade Agreements Act of 1979 (TAA), as amended, 19 U.S.C. § 2501 et seq., requires the federal government to procure only goods that are “domestic end products,” or “designated country end products,” unless an exception applies. TAA compliant products are those that are manufactured or "substantially transformed" in the United States or in a TAA designated country with which the U.S. maintains a trade agreement and regards as a reliable or acceptable procurement source.
Page
Self-monitoring Systems & Redundancy | Ultimate Reliability
Self-monitoring and redundant systems Ultimate Reliability Symphony Platform In critical situations, every second – and every word – counts. Commend systems are designed specifically to ensure that every single call gets through, no matter what. Always, without exception. This is why Commend systems monitor their own functionality: Line Monitoring checks the connections between the Intercom stations and the Server. The Intercom stations run continuous tests on the signal path between their loudspeaker and microphone. More Self-testing buttons for critical functions perform regular button activation simulation tests (special buttons are required). To protect Intercom stations against vandalism, sabotage detection switches will trigger an alarm at the Control Desk if the device is tampered with. Server monitoring and redundancy ensure the required high availability. Promises you can rely on Full 24/7 availability. Control Desk staff are immediately notified in the event of a problem (e. g., extreme vandalism) to enable instant troubleshooting. Very low system inspection requirements – no need for manual testing (saving time and costs). Software Intercom Server VirtuoSIS Entire virtual environments can be backed up and migrated reliably without interruptions. As a result, scheduled downtimes are a thing of the past. After an unscheduled downtime, connections and functions are restored within a very short time. Ultimate availability ‒ ultimate security (Mirroring*) *Mirroring: VMWare Enterprise Edition provides a Fault Tolerance (FT) function to ensure continued availability for all applications in case of a server failure. VirtuoSIS Server redundancy for hardware-based Intercom Servers Intercom stations can connect to up to three servers simultaneously. Calls are transmitted via the active server. Fallback servers within the network allow for reliable redundancy arrangements. In the event of a server or router failure, call connection will be re-routed automatically via the available servers. Multiple power supply units ensure a redundant supply of operating power. This way, the Server will continue to operate uninterrupted even if a power supply unit fails. Hardware Servers Server redundancy for SIP capable systems Intercom stations can connect to up to three servers simultaneously. Calls are transmitted via the active server. In case none of the servers can be reached, the system can try to establish a serverless connection as a last resort ‒ e.g., by setting off a call to all Intercom stations on the network. Of course, this is also supported by serverless systems. High Availabilty Every single call gets through, no matter what.
Page
Intelligent Volume Control | Automatic Level Adjustment
Sound volume that adjusts dynamically to the level of background noise Intelligent Volume Control – IVC Perfect Speech Intelligibility A special audio processing method developed by Commend, IVC enables Intercom stations to ‘listen’ for background noise and adjust the station’s sound level accordingly . As a result, the volume level automatically matches the ambient noise level by going up or down, thus maintaining precisely the level that is most comfortable for the human ear. This way, the helpful voice of the operator is easy to understand at the tunnel emergency station despite the deafening traffic noise in the background. The same applies to the Intercom station in the production hall, where Intelligent Volume Control ensures that critical announcements and instructions cannot get lost in the background noise If the noise becomes more, then the volume increases automatically It is not possible to reduce the noise for the person on site, but in order for them to understand the other party immediately , Intercom stations, modules and loudspeakers automatically increase the volume so that everything is clearly understood. Comfortable volume level in silent environments On the other hand, you can avoid deafening announcements or conversations. This is because one does not set the standard volume to what could be possible noise sounds, but to a comfortable volume. IVC does the rest. The clarity and intelligibility of Intercom communication does not only depend on the quality of the speech signal being transmitted. The other essential criterion is how well the Intercom station is able to adjust to its surrounding conditions. Commend Intercom stations stand the test of everyday use in a variety of different environments. The acoustic spectrum ranges from absolute silence to extreme noise. Ensuring optimum intelligibility even under extremely noisy conditions is a very special challenge. With Intelligent Volume Control (IVC), our audio engineers have come up with a unique solution. IVC delivers voice messages in superior quality and clarity, even through the thickest veil of background noise. At the same time, it ensures that the voice signal always arrives at a comfortable volume level, even if there is low background noise. IVC is a critical function for many devices and applications – from the emergency call station in a road tunnel to the industrial Intercom station in a production hall. Speech Intelligibility