Results (1373 found)
News
From Input to Insight: Centralised Monitoring for Enhanced Security
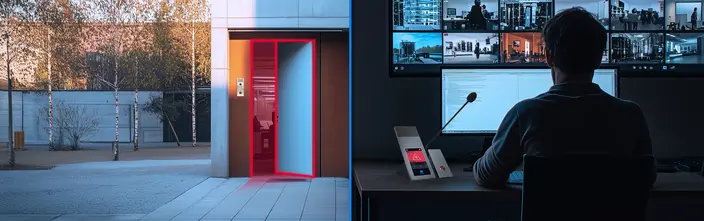
We are excited to introduce a new enhancement in our Symphony Control Desk solution that significantly improves operational efficiency and incident awareness. With this update, our system can now display input messages and line fault messages through distinct visual and acoustic signals . Imagine being in charge of a huge office building with multiple wings and doors - you want to ensure everything is safe and secure, especially when the building is unoccupied. The Symphony Control Desk can now receive input messages, such as open windows or doors, particularly in sensitive areas. These messages can be categorized into two types: informational messages , which provide a heads up, and alarm messages , which signal a more severe issue. With our ComPLC tool, users can even create custom logic, for example automatically triggering an alarm when two signals are triggered simultaneously. The system also alerts operators to line fault messages , which occur in the rare case that a device goes offline, e.g. due to a power outage or other issue. The goal of this enhanced functionality is to enable even better remote monitoring , allowing control desk operators to identify and address discrepancies throughout the building from a central location. This is not limited to the example of a big building. It can be applied to various scenarios , like as international car parks, where input messages can monitor pedestrian doors, barriers, and ticket machines. By leveraging input messages, the Symphony Control Desk provides an overview about the current state of the system and minimizes the need for human intervention , except when necessary for remediation. This streamlines processes and maximizes efficiency, making it an essential tool for organizations that prioritize security, monitoring, and maintenance. The Symphony Control Desk is designed to provide a single, unified view of an organisation’s security and operations , allowing operators to respond quickly and effectively to any issues that arise. Overall, it is a powerful tool that helps to keep organizations safe, secure, and running smoothly. It's like having a virtual guardian that keeps an eye on everything and alerts you to any problems, so you can take action to fix them. By providing real-time monitoring and automated alerts, the Symphony Control Desk helps organizations reduce risks and improve their overall security posture .
Page
10 Recommendations | Risk Assessment Guide
We recommend considering the following points when conducting a risk assessment Risk Assessment Cyber Security Security requirements and objectives , e.g., function-specific and non-function-specific system requirements System or network architecture and infrastructures , e.g., using a network map and component plan that show how assets are configured and interconnected Services and applications , including data and protocols, e.g., applications with particularly sensitive data Processes regarding data processing , including input and output parameters, such as business processes, computer operating processes and application operating processes Dependencies between applications and processes , e.g., processing of particularly sensitive data Impact assessment , e.g., identification of consequences in case of loss of sensitive data, model-assisted threat analysis, etc. Technical measures , e.g., selection of suitable security components, such as firewalls, intrusion detection systems, or physical and logical access control systems Organisational measures , e.g., business continuity management and desaster recovery management Government laws and regulations pertaining to minimum security control requirements Documented or informal policies, procedures and guidelines For further information, please refer to Information Systems Audit and Control Association, ISACA ( www.isaca.org ) or the corresponding ISO standard for Risk Management in IT Systems ISO 27005. Cyber Security
Page
Infrastruktúra-opciók – a helyszíni megoldásoktól a felhőig
Infrastruktúra lehetőségek Helyi? Felhő? Kombinált? Nincs szerver? A választás a tiéd Symphony Platform Lehetőség van kizárólag felhőalapú infrastruktúra használatára, helyszínen vagy adatközpontban üzemeltetett szerverek alkalmazására, illetve ezek kombinálására is. A méret és az igények függvényében egy szerver nélküli, Symphony Mesh alapú megoldás is választható. Ez a választási lehetőség a meglévő rendszerek esetében is elérhető. Ügyfeleink ismerik és értékelik a Commend Evergreen technológiát, amely lehetővé teszi számukra, hogy rendszereiket a legújabb technológiához csatlakoztassák, és a legmodernebb infrastruktúrán működtessék. Symphony Cloud On-Prem Mesh Bridge Áttekintés 60 másodpercben Az Intercom jövője Symphony Cloud Felhőalapú megoldási platformunk rendkívül jól skálázható felhőinfrastruktúrára, nagy teljesítményű szoftverre és átfogó funkciókra épül, egyértelmű céllal: a jelenlegi és jövőbeli felhőszolgáltatások – beleértve a mesterséges intelligenciát – lehetőségeinek kiaknázása. A Symphony Cloud minden mérethez és igényhez a megfelelő szolgáltatást kínálja. A megoldások lehetnek teljes mértékben felhőalapúak, vagy helyszíni szerverekkel kombináltak. Jelenlegi felhőszolgáltatások: Eszköz- és rendszerkezelés Mobil kliens iOS és Android alkalmazásokkal Webes kliens böngészőkhöz, vezérlőpult funkciókkal Ivy – virtuális Intercom hangasszisztens Tudjon meg többet Megbízhatóság házon belül Symphony megoldás helyben A Commend VirtuoSIS, a világ első teljesen szoftveralapú Intercom szervere lehetővé teszi, hogy megoldásaink zökkenőmentesen illeszkedjenek a virtuális IT-környezetek (VMware vSphere, Microsoft Hyper-V és Nutanix Acropolis) rugalmas és dinamikus világába. Ugyanez a technológia képezi a Commend S3/S6 hardveralapú szervereinek alapját is, ahol minden előnyét és technikai képességét kamatoztatja: maximális funkcionalitás és üzletileg kritikus magas rendelkezésre állás – ezek a Commend megoldások meghatározó jellemzői. Helyszíni funkciók: Átfogó lehetőségek és funkciók a vezérlőpultok kezeléshez (hardveres és szoftveres megoldások) Teljes interfész- és integrációs lehetőségek, vezérlés és automatizálás – Integrációk Minden adat az ügyfél telephelyén (vagy adatközpontjában) marad Felhőszolgáltatások szolgátlatások Symphony Bridge segítségével Több mint 50 év fejlesztési tapasztalatának funkciókészlete VirtuoSIS rendszerről Autonóm és intelligens Symphony Mesh A legújabb „Symphony MX” és „Symphony BF” generációs Commend eszközök elegendő beépített intelligenciával rendelkeznek ahhoz, hogy ne legyen szükség külön szerverre. Szabad, közvetlen hálózatban működve intelligens, autonóm kommunikációs hálózatot alkotnak (regisztráció nélküli működés), amely költséghatékony, és ideális kisebb méretű alkalmazásokhoz. A Commend Intercom rendszerek átfogó funkcionalitása olyan lehetőségeket kínál, mint a hívásfogadás és -továbbítás, videó, távvezérlés, Unified PA, redundancia és sok más. Ezek lehetővé teszik az egyedi megoldások kialakítását az üzemeltetési és biztonságkritikus alkalmazások és folyamatok támogatására. Különösen az egyedülálló, úgynevezett „műveletsorozatok” teszik lehetővé, hogy a Commend IP eszközök olyan funkciókra és vezérlésekre legyenek programozhatók, amelyekhez normál esetben jelentős szerveres háttér lenne szükséges. Symphony Mesh részletek Erőteljes kapcsolat Symphony Bridge A Bridge lehetővé teszi, hogy a helyszíni megoldások világa összekapcsolódjon a Symphony Cloud szolgáltatásaival, például a mobil iOS és Android kliensekkel, valamint akár egy böngészőablakban kényelmes híváskezelést biztosító Web klienssel. A két architektúra kombinálása teljesen új megoldásokat tesz lehetővé, amelyek a két világ legjobbjait egyesítik. A felhőben sehol sem halad gyorsabban az innováció. Számos izgalmas fejlesztés van tervben, a következő Symphony szolgáltatások már fejlesztés alatt állnak vagy kiválasztott pilotprojektekben kerülnek tesztelésre. A Symphony On-Prem és a Symphony Bridge segítségével ez az új lehetőségekkel teli világ csupán egy kattintásra van. Tudjon meg többet
Page
All-around Cyber Defense | Secure Communication Systems
All-around Cyber Defense for Products and Applications Commend Defense In-Depth-Strategy Cyber Security Commend Defense In-Depth-Strategy is based on the principle of ensuring IT security in all areas (environments, design, implementation and integration) to eliminate vulnerabilities and attack vectors. In practice, this means: IEC ISO 27001:2022 certified , company-wide information management system ( Learn more ) World’s first Intercom company certified to IEC 62443: Tested and certified by globally recognized cyber security certification service provider TÜV SÜD Commend development teams develop and implement secure communication and automation solutions in accordance with the IEC 62443 Part 4-1 ( Learn more ) Use of secure standard Internet protocols: TLS and SSH data transfer security for HTTP and MQTT Secured SIP network access via 802.1x auth and 802.1q VLAN connections Use of secure cryptography by default: Encrypted, login-protected communication via Commend signed device certificates Commend Public Key Infrastructure (PKI) as a basic ‘Root of Trust’ (for generating and signing of device and application certificates) to ensure mutually login-protected, encrypted communication Security-focussed development processes: Multi-level monitoring and testing Regular test cycles before product releases and after updates Vulnerability monitoring and disclosure policy: Pen tests by external security testing bodies or ethical hackers Coordinated processes for reporting and disclosing vulnerabilities Commend Security Advisory Program: summaries of notifications, affected products, software updates, workarounds or mitigation, change log, etc. The global security-specific hardening of local and cloud-based Commend systems spans several basic levels: Devices Data Applications Platform Device Security Physical access protection Vandal-resistant Video Intercom stations (with camera) Tamper detection via electromechanical contact USB and port debugging protection Access Control Systems Secured network access 802.1q VLAN standard (network segmentation) 802.1x secured login Commend IP Secure Connector (automatic network cut-off in case of manipulation) Terminal device security Offline capability, includes SIP call and door call functions Unique system login credentials for each individual device SSH remote maintenance functions disabled by default SHA and BCRYPT salted passphrase, encrypted access credentials Back to overview Data Security Data transfer protection Encrypted, login-protected communication settings TLS v1.2+ used exclusively with Secure Cipher Suites (> 128-bit) X.509 ECC NIST P-384 Commend device certificates Protection of stored data Use of MS Azure for database and data storage via PaaS Secured access to Azure data storage via device-specific SAS tokens Powerful 256-bit latest-generation AES data encryption SHA and BCRYPT salted password hashes (> 256-bit) Back to overview Application Security VirtuoSIS application security Offline capability, includes SIP call and door call functions Support of multiple instances: enables service redundancies as an emergency fallback solution Application security for devices Offline capability, includes SIP call and door call functions Enforced change of default login credentials upon first login Password minimum requirements: 12 characters Detection of brute-force login attacks Secured network ports Back to overview Platform Security Cloud platform-security OAuth Identity and Access Management (IAM) Azure Security Center Monitoring Azure KeyVault Secrets Management Azure Storage Service Encryption (SSE) Database Transparent Data Encryption (TDE) Open source and vulnerability management Use of proven de-facto standard libraries for logins and encryption Contribution to open source applications (e.g., Asterisk, BareSip, Mosquito, Wireshark) Continuous vulnerability scanning and monitoring Commend Security Advisories Secure default Internet protocols with focus on compatibility and security Back to overview
Page
NDAA and TAA compliant Intercom Systems
Trusted. Communication. Always. For Better Serving the US Public. Commend Intercom Systems Fully NDAA/TAA-Compliant Cyber Security In line with its strong corporate commitment to providing “Trusted. Communication. Always.”, Commend invests a lot of care and attention in ensuring product security both on the hardware and software level. Commend components, products and solutions are developed and manufactured from the ground up on the principle of “Privacy and Security by Design”. This is evidenced by a series of relevant audit-based certifications. They range from full ISO 27001 certification of the entire R&D and production environment to IEC 62443-4-1 for specific development processes. Existing or potential customers of Commend Americas that rely on this high level of product security include governmental agencies such as the U. S. Department of Defense or its affiliates. To them Commend USA is pleased to confirm that its entire product portfolio is in full compliance with the National Defense Authorization Act (NDAA) and the Trade Agreements Act (TAA). Full NDAA/TAA compliance is ensured on several levels: All products are produced exclusively at the Commend facilities in Salzburg, Austria, which eliminates the need for OEM sourcing. Commend has extensive product development policies and guidelines in place, which explicitly cover the NDAA requirements (among many others). All software used for and in Commend products is developed and implemented in-house in accordance with stringent and regularly audited cyber-security standards. Commend USA, through its related company, Commend International GmbH in Salzburg, Austria, certifies compliance of its product portfolio with all applicable requirements under NDAA/TAA . Certificates & Declarations What is NDAA? The National Defense Authorization Act (NDAA), specifically under Sections 889(a)(1)(A) and 889(a)(1)(B), imposes a prohibition on federal agencies, their contractors and grant or loan recipients to procure or use certain “telecommunication and video surveillance equipment or services” from specific Chinese companies. The banned items must not be used in “a substantial or essential component of any system, or as critical technology as part of any system.” This ban covers telecom products produced by (among others) Huawei Technologies Company and ZTE Corporation, and video surveillance and telecom equipment produced by Hytera Communications Corporation, Hangzhou Hikvision Digital Technology Company, or Dahua Technology Company. What is TAA? The Trade Agreements Act of 1979 (TAA), as amended, 19 U.S.C. § 2501 et seq., requires the federal government to procure only goods that are “domestic end products,” or “designated country end products,” unless an exception applies. TAA compliant products are those that are manufactured or "substantially transformed" in the United States or in a TAA designated country with which the U.S. maintains a trade agreement and regards as a reliable or acceptable procurement source.
Page
Secure Product Development Lifecycle | IEC 62443
World's first Intercom Company certified to IEC 62443 standard Secure Product Development Lifecycle Cyber Security At Commend, we have always known when it comes to Cyber Security , there is no simple solution that covers all security needs. Regardless of the size of a Commend system and the underlying network infrastructure, Cyber Security is a cooperative effort that requires the collaboration of all stakeholders along the entire product supply chain , from the vendor to the end user. The successful certification according to IEC 62443-4-1 underlines the importance of "Secure-by-Design" as an integral part of Commend's product development. It's not just about what tools to use or what actions to take, but what to use them for (or against) and when, how, and where to implement them. It's about identifying potential risks and targets, understanding threats, and taking action to counter them. As part of our defense-in-depth strategy, cyber security is firmly embedded at Commend and we sustainably support our customers' security strategies . To not only claim this, but also prove it to an independent auditor, we decided to certify to IEC 62443 Part 4-1 . This certification by the globally recognized Cyber Security certification service provider TÜV SÜD confirms that our development teams can develop and implement secure communication and automation solutions in accordance with the IEC 62443-4-1 standard and that our "Security by Design" guidelines meet the high requirements for secure automation solutions for Industry 4.0! Our ultimate goal is a systematic, responsible risk management on all levels based on the principle of ‘Privacy and Security by Design’ In practice, this implies keeping to the strict CIA Information Security Goals: Sustainable protection and confidentiality of customer data and communication Integrity of systems and communication lines High availability of all products and services Cyber Security
Page
ISO 27001 Certification | Information Security Management
We develop in full compliance with IEC ISO 27001 Cyber Security Begins at Home Cyber Security At Commend cyber security begins in our own organisation, and it shows in the way we develop our hardware and software: in full compliance with strictly certified IEC ISO 27001 standards, based on a company-wide Information Security Management System (ISMS). IT security is not a technical status or condition, but rather the visible expression of a responsibly held commitment. Only those who practice IT security themselves can expect to be trusted to provide it. An ISMS provides a systematic approach to managing sensitive corporate information in order to ensure the security and protection of the organisation’s data assets. At Commend International, our ISMS drives a continuous risk management process that takes everything into consideration, from our staff to our corporate processes and IT systems. Since end-2019, Commend International GmbH has been the world's first fully EN ISO 27001 certified intercom company, including our entire operations and all development teams. As a result, cyber security is always on our mind, as it’s become part of our corporate DNA makeup – and one of our core competences. It determines the way we develop our products, the selection of IT technologies we incorporate in them, and the way we live up to our commitment to providing regular updates and new IT security fixes. Our ultimate goal is a systematic, responsible risk management on all levels based on the principle of ‘Privacy and Security by Design’ In practice, this implies keeping to the strict CIA Information Security Goals: Sustainable protection and confidentiality of customer data and communication Integrity of systems and communication lines Cyber Security High availability of all products and services
Page
The Commend Art Project
The Commend Art Project Where Art and Communication Speak the Same Language A Vision Rooted in Passion Every great idea begins with a spark. For Commend, that spark came from Peter Pablik – founder, brilliant engineer, and lifelong art enthusiast. In the 1970s, Mr. Pablik began collecting works from local Salzburg artists, weaving creativity into the very DNA of the company. What started as small, handcrafted gifts for customers – limited-edition art prints born from local collaborations – soon evolved into something greater: A celebration of art as a way to make deep connections with others. Thus, the Commend Art Project was born: a dialogue between creativity and communication, technology and emotion, innovation and craftsmanship. Milestones of a Living Tradition By the 1980s, the project had taken a new form – the Commend Art Calendar . From an initial 50 copies to several hundred, the calendar traveled the world, carrying the spirit of Salzburg’s artistry into homes and offices across continents. A turning point came in the late 1990s. During a year-end meeting between Commend’s managing director and the bank advisor, it turned out that both had given away the same calendar by artist Bernhard Vogel as a gift – one with the Commend logo, the other with the bank’s logo. This awkward coincidence led to a revelation: Commend’s Art must be unmistakably its own. From that moment onward, Commend curated every detail in-house: Handpicked artists Individually chosen artworks Defined editions Complete creative and production control The result: a calendar that doesn’t just mark time – it creates moments . Art as a Language of Connection For project director Wolfgang Peer , who has guided the initiative since 1986, the essence of the Commend Art Project lies in its power to open conversations . Art transcends words – yet it inspires them. It creates visual and emotional spaces where people engage, connect, and remember. This is the perfect mirror of Commend’s core philosophy and brand essence: Communication is connection. Each calendar serves as a daily reminder that keeps Commend in the minds and conversations of its partners. Every single copy embodies the company’s values: Uncompromising quality Authentic craftsmanship Thoughtful materials Exceptional artistic talent Communication as a living art form Regional roots. Global resonance. By working with Salzburg artists, Commend celebrates its heritage while giving regional talent an international platform – often leading to new commissions and collaborations worldwide. Two Pillars of Artistic Expression 1. The Commend Art Calendar – Art that Travels the World Strictly limited annual edition (currently 2,200 copies ) Distributed globally to clients, partners and Commend teams Available exclusively through Commend Accompanied by an artist-signed certificate of authenticity Each calendar is a limited-edition collector’s piece – a bridge between art, brand, and human connection. 2. The Commend Edition – Art in its Purest Form One unique artwork each year Limited to 250–280 signed and numbered prints Originally etchings and lithographs, now also digital fine art prints Presented as an exclusive and festive year-end gift to selected recipients A Living Legacy of Art and Connection Over the years, the Commend Art Project has grown into far more than an artistic initiative – it has become a beloved ritual shared by partners, clients, and friends around the world. In countless offices and homes, there is something quietly symbolic: a “Commend calendar nail.” Each December or January, it marks a small yet meaningful ceremony – the gentle moment when the old calendar gives way to the new. A fresh set of images, a new year of inspiration. This simple act has become a tradition that connects people across countries and cultures – a silent rhythm of renewal, art, and communication. The ongoing enthusiasm, the heartfelt messages, and the enduring presence of these calendars in daily life all speak to the project’s essence: art as a language of trust and connection. Through decades of creativity, craftsmanship, and collaboration, the Commend Art Project continues to embody what the brand stands for – quality, authenticity, and communication that endures. Because at Commend, one truth always remains: Trusted. Communication. Always. Wall of Fame Commend Art Calendar 2005-2025
Page
Project Consulting Commend India
Project Consulting How can we help you? Your ideas. Your requirements. An overall solution. Are you looking for assistance with a new project? Do you have a technical question or need help in deciding how to expands your existing system? Contact us to take advantage of our comprehensive range of services. If you are on the lookout for an individual security/communication solution We provide individual advice on finding the best security and communication solution to suit your requirements. We will work with you to develop a plan for your individual system solution. You can take full advantage of our long-standing experience resulting from more than 150,000 installations worldwide. We will support you all the way in implementing your solution, taking care of the individual steps. Users will receive full training from our experts to ensure your system will run smoothly and is used to its full potential. Of course, we also provide a wide range of system maintenance and servicing options, as well as technical support whenever you need it. If you intend to extend your existing system Uncompromising backward compatibility is a hallmark of our systems. It allows for extending existing legacy systems with latest technology, even enabling full networking of sites running different systems. We provide assistance in planning and installing extensions and take great care to ensure long-term economical efficiency. If you need a custom station or software We design and manufacture intercom stations and emergency call points according to your requirements – whatever these are (Features, Material, special Size e.g. for existing back boxes). We write special software for ComWIN and the Intercom Client, browser interfaces, ... We programme interfaces to other systems. Learn more about our Customized Solutions Support Constant availability is essential in security and communication systems. You can rely on us being there whenever you need assistance. Our worldwide technical teams are standing by to provide telephonic or on-site support at any time, quickly and reliably. Contact us Training Sign up for our expert training course and become a Commend System Professional. Your local Commend Partner will be glad to provide further details on our course schedule. Training area Software & Documentation Leverage our on-line knowledge base as an extensive reference to find answers to your questions. Here you have access to important information about our systems, from installation instructions to hints on how to optimise your configuration and download links to current software versions. cLibrary 23 Sales Organisations worldwide Always there, wherever you are America – Europe – Africa – Middle-East – Asia/Pacific
Page
Audio Modes | Perfect Speech Intelligibility
Perfect Speech Intelligibility Audio Modes Overview Intercom Stations support three audio modes OpenDuplex ® operation: maintains open communication lines in both directions to allow for natural, fully hands-free conversations. Switched Duplex operation: detects and switches the communication direction automatically. Simplex operation (PTT = Push to Talk): allows for manual control of the communication direction; a button must be pressed before speaking. Commend’s OpenDuplex ® technology includes a powerful echo cancellation algorithm to improve speech quality, even in 16 kHz eHD Voice audio quality. Actual distance: 3,935 km // Felt distance: 1 m Customer in Perth 22:47 Incoming call from a car park in Perth. A customer is having difficulties paying with her credit card at the exit gate. Call Center Sydney 22:48 The call centre agent responds to the request by talking the customer through the payment process, then wishes her a nice evening. A natural communication experience as loud and crystal clear as a face-to-face conversation made possible by a Commend Intercom system. Open Duplex for Natural Conversations This type of speech control allows simultaneous talking and listening and provides top quality speech intelligibility. The conversation is permanently switched through in both directions, therefore both conversation partners can speak simultaneously. The OpenDuplex ® mode allows an improvement in speech quality at high ambient noise levels. OpenDuplex ® is carried out by Echo Cancelling in the station. Should not be confused with Full-Duplex which is similar but without echo cancelling and therefore only works correctly when one side is using a gooseneck microphone or headset. Switched Duplex With this type of speech control, a duplex controller controls the direction of speech. Only one person can speak at a time. Speech communication in both directions, in which the louder sound source (usually the speaking person) determines the direction of the speech connection. This means the loudest side speaks and the other listens. Perfect intelligibility up to a distance of 7 meters from the station, without pressing a button – the distance depends on the ambient noise. The speech direction is determined by the “speech balance” (duplex controller). Simplex This is the earliest type of speech control where the speech direction is controlled manually. Only one person can speak at a time. Speech communication only in one direction that is controlled by pressing the talk button. Also known as press-to-talk, release to listen. Simplex is used for manual speech control, e.g. areas with high ambient noise. Possible configuration: Conversations fixed Simplex (the speech direction after initiating a conversation can be defined). Simplex by pressing a button (the button must be held down to talk and released to listen). Simplex by momentarily pressing a button. The other person must press the button to reverse speech direction. Perfect Speech Intelligbility